
Resources
Do I Pay the Ransom? Insights from an Incident Responder
"Should I pay the ransom if I am attacked?" Insights gathered while working with companies that faced these questions.
Ransomware Resilient Backups
SecurIT360 shows you how to avoid being a victim of ransomware attacks by creating proper backups.
Understanding CMMC
Explore the essentials of CMMC, its cybersecurity impact, compliance levels, and how it protects defense contractors.
MSP vs. MSSP: What’s the Difference, and Why It Matters
Discover the key differences between MSPs and MSSPs, their roles in cybersecurity, and how to choose the right one for your business needs.
Why AI Won’t Replace Your SOC
AI is a powerful tool for security operations, but it can't replace the human judgment a SOC depends on when the unexpected happens.
Finding: DNSSEC Not Enabled on Azure DNS Zones
Secure your domains by learning how to enable DNSSEC on Azure DNS Zones. Step-by-step guide to boost DNS integrity.
Remediation Plan: Strict Transport Security Not Enforced (RFC 6797 – CWE-523)
Learn how to create a remediation plan for CWE-523 by enforcing HTTP Strict Transport Security (HSTS) per RFC 6797.
The Rise of Ransomware-as-a-Service: A Roadmap For Executives
Ransomware-as-a-Service operates like a traditional SaaS. Affiliates pay a subscription fee or share a percentage of the ransom profits.
7 Questions Security Leaders Should Ask After a Penetration Test
Learn the 7 critical questions security leaders must ask after a penetration test to turn findings into action and strengthen cyber defenses.
OWASP Top 10 Part 3: Software Supply Chain Failures — From SolarWinds to Vibe Coding | Episode 189
In this episode, the conversation focuses on software supply chain failures, now a top concern in the OWASP Top 10. Real-world examples and practical strategies are discussed to help organizations manage the risks of using third-party components and vendors.

Episode 188: Guaranteed Way to Catch Threat Actors
In this episode, we break down how deploying cyber deception and honeypots can give defenders the upper hand against threat actors. Learn actionable strategies from active internal pen testers on guaranteeing early detection and improving your blue team’s effectiveness.

Episode 187: Avoid This Cyber Leadership Trap
Avoid one of the biggest mistakes in cybersecurity leadership: buying tools before having a strategy. This episode breaks down a smarter approach that ensures security investments actually solve the right problems.

Episode 186: Real-Life Active Directory Attack Paths
Join us as we break down real-life Active Directory attack paths uncovered during internal penetration tests. Learn how attackers exploit common misconfigurations and what you can do to defend your environment.

Episode 185 | A Toddler with a Bazooka: The Real Risk of AI Agents
AI agents have moved far beyond chatbots and are now deeply woven into business operations, bringing new levels of risk and complexity. In this episode, we cut through the hype and break down what IT and security teams actually need to worry about.

Episode 184: Active Directory Isn’t Dead. It’s Just Undefended
Active Directory isn’t dead—it’s still powering the majority of organizations, and security risks are as critical as ever. In this episode, we dig into the real facts, common attack paths, and actionable defense strategies.

Episode 183: OWASP Top 10 Part 2 – Security Misconfigurations That Get You Hacked
In this episode of The Cyber Threat Perspective, we continue our breakdown of the OWASP Top 10 by focusing on security misconfigurations. Learn why these vulnerabilities are common, how they happen, and what you can do to avoid them in your own web applications.
Episode 182: Patching Crisis — Vulns Now #1 Attack Vector (2026 Verizon DBIR)
The 2026 Verizon Data Breach Investigations Report is out, and it’s time to break down what really matters for IT security teams. In this episode, we cut through the noise to highlight the new trends, major shifts, and actionable insights you need to know right now.

Episode 181: AI Zero-Days (Google Threat Intelligence Report)
Google’s Threat Intelligence Group just dropped a game-changing report on the role of AI in modern cyber attacks. In this episode, we break down what’s new and what it means for defenders and organizations.

Episode 180: Cybersecurity Echo Chambers — How to Think Critically in a Hype-Driven Industry
In this episode, we break down the dangers of echo chambers in cybersecurity and the importance of critical thinking in a hype-driven industry. Learn practical strategies to avoid falling into groupthink and make smarter decisions for your organization.
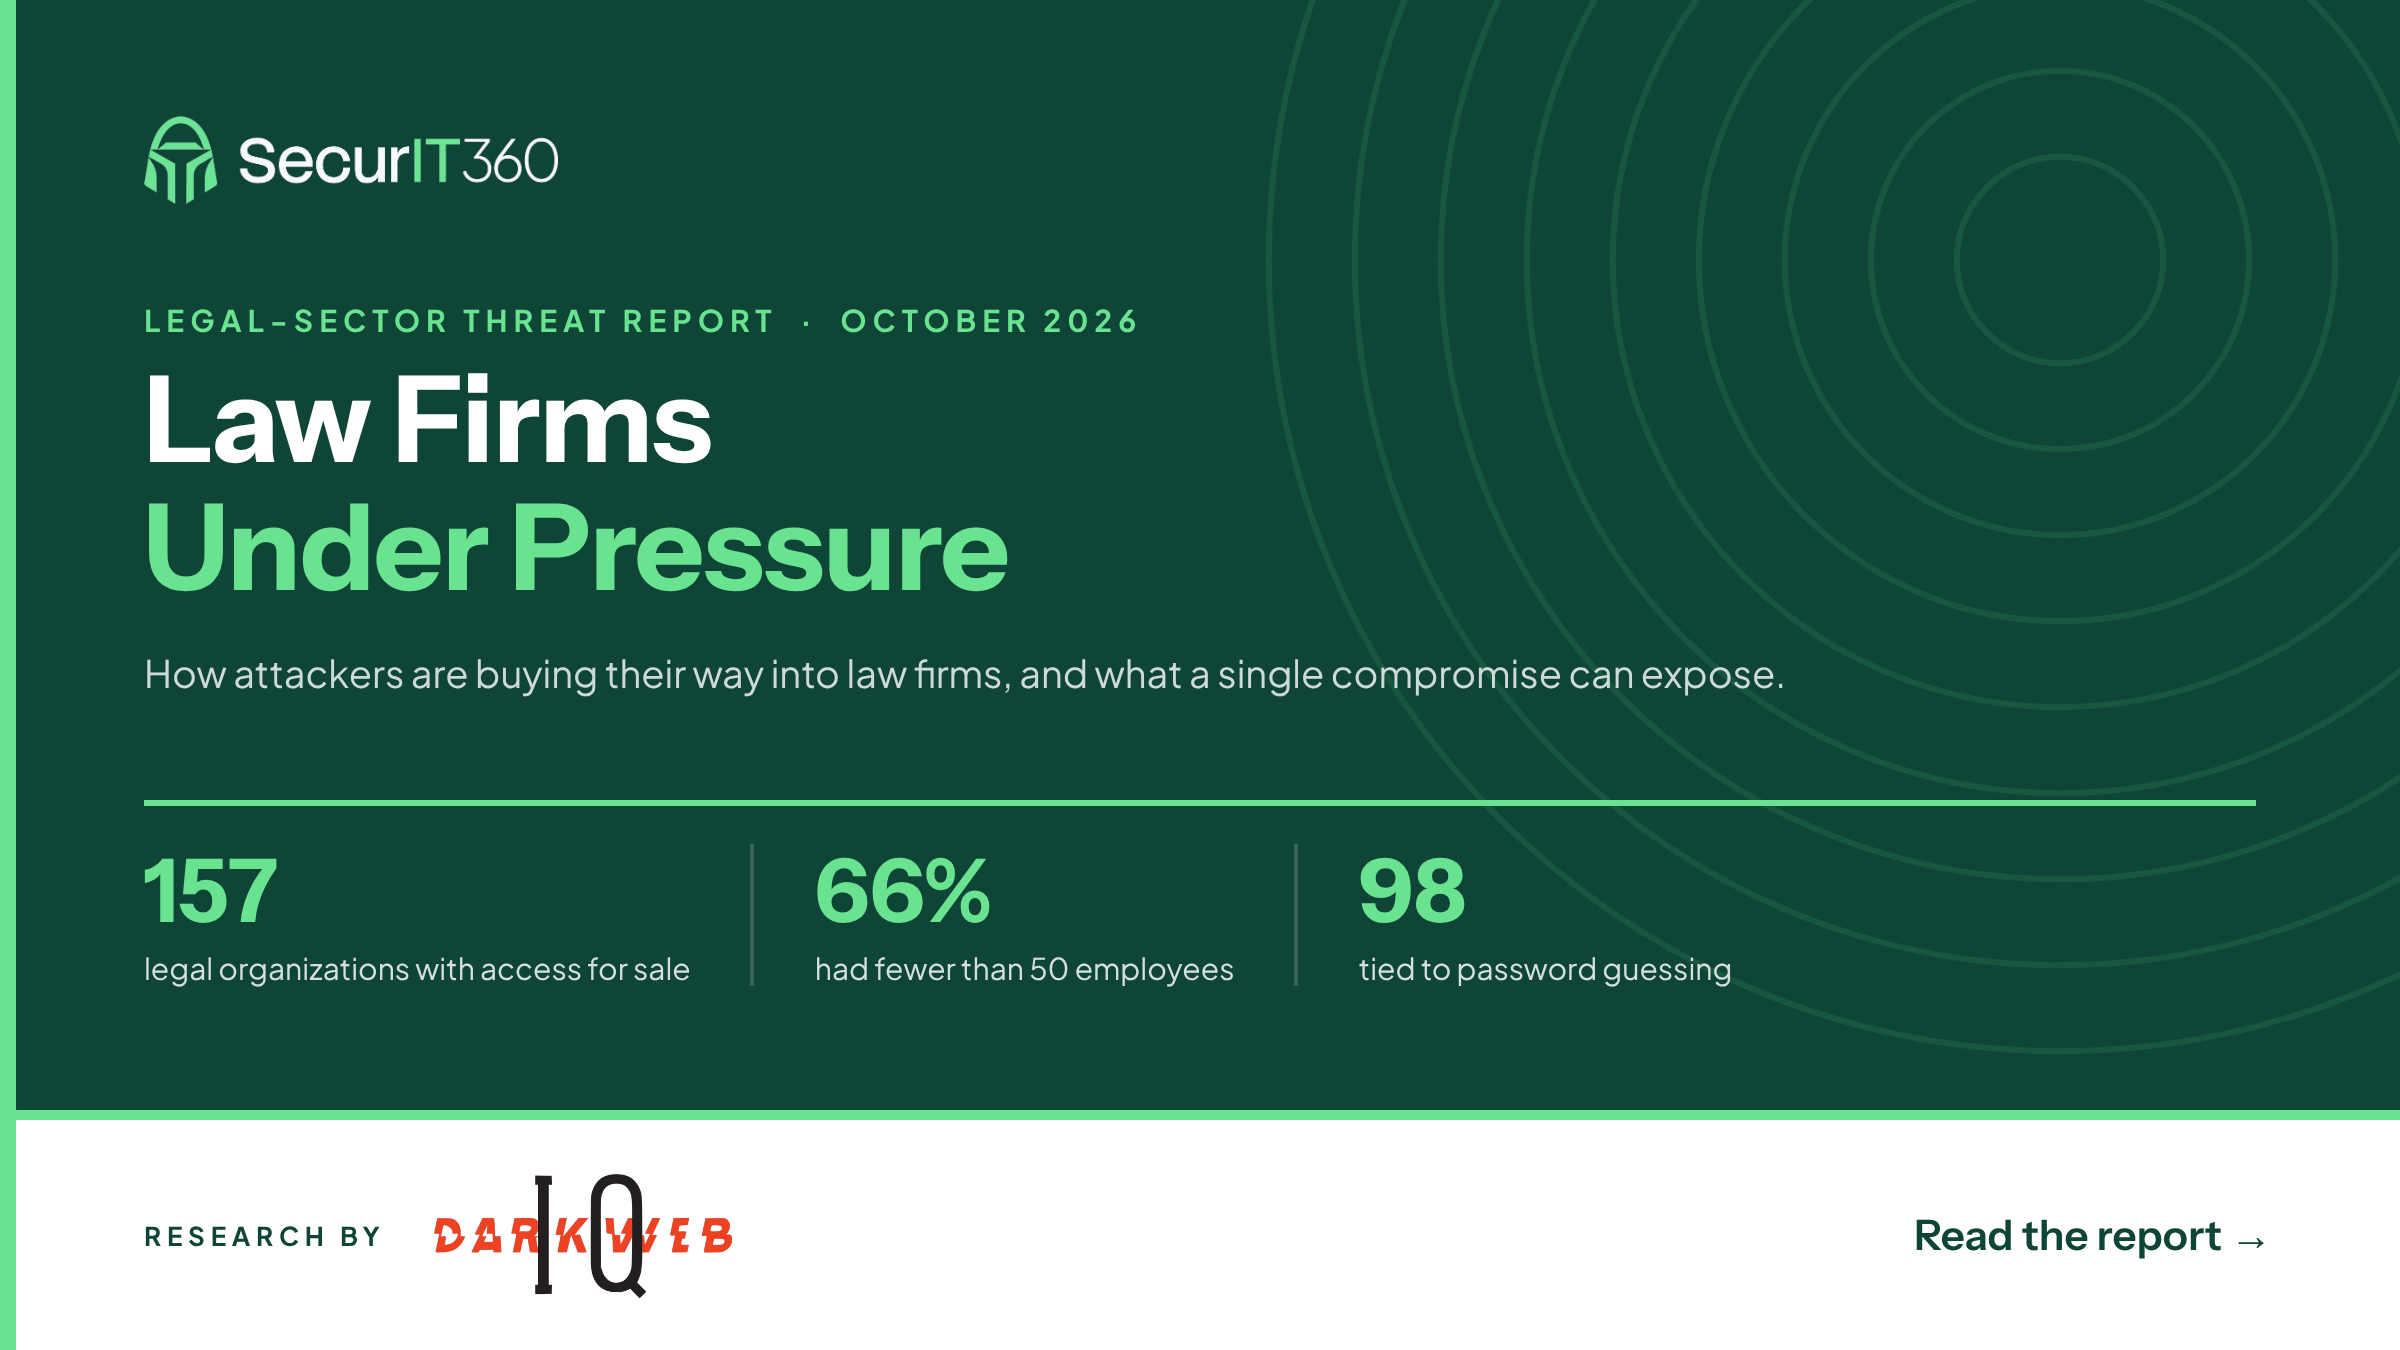
Law Firms Under Pressure: Legal-Sector Threat Report
Darkweb IQ research on 157 legal-sector organizations whose network access was offered for sale, and what a single compromise can expose.
10 Things You Should Be Doing in AI Security
A practical checklist of ten steps law firms should take to secure AI use, from governance and tool inventory to access controls, testing, and monitoring.
Professional Services: 2026 Cyber-Threat Landscape
Professional services was the second-most-breached industry in 2026, and the only major target left unprofiled in the year's most-cited breach research. Our executive summary fills that gap, translating the data into what it means for legal, accounting, consulting, and engineering firms.
AI Security Isn't New. Your Gaps Are.
Most law firms don't have an AI security program. They have an AI security document. Learn why governance, testing, and monitoring must work together to protect privileged data and reduce AI risk.