Security that holds up
across your entire operation

Enterprise-grade expertise, built for how your team actually works.

We combine disciplined assessment, objective guidance, and continuous protection. Stay secure, resilient, and prepared without unnecessary complexity.

Talk to an Expert

Security built for
real-world operations

View Our Solutions

Most organizations don’t need more security tools. They need confidence that their business can keep operating when something goes wrong.

SecurIT360 helps organizations build security programs that support continuity and resilience –combining monitoring, testing, and expert guidance into a coordinated approach.

View Our Solutions

ContinuousSecurity Validation (PenGarde)

Know where you’re exposed – every day, not once a year. Ongoing testing identifies real-world attack paths and helps ensure your defenses continue towork as your environment evolves.

Learn about PenGarde

Managed Detection & Response

Maintain visibilityand respond quickly, without overwhelming your team. We monitor, investigate, and act so your operations stay uninterrupted.

Explore MDR

Offensive Security

Understand where your organization is truly exposed. Expert-led penetrationtesting simulates real-world attacks to uncover risk across systems, applications, and cloud environments.

Learna bout PenGarde

Incident Response

When something goes wrong, clarity matters.We help you contain threats, coordinate response, and restore operations quickly, so your business can keep moving.

Learna bout PenGarde

ContinuousSecurity Validation (PenGarde)

Know where you’re exposed – every day, not once a year. Ongoing testing identifies real-world attack paths and helps ensure your defenses continue towork as your environment evolves.

Learn about PenGarde

Managed Detection & Response

Maintain visibilityand respond quickly, without overwhelming your team. We monitor, investigate, and act so your operations stay uninterrupted.

Explore MDR

Offensive Security

Understand where your organization is truly exposed. Expert-led penetrationtesting simulates real-world attacks to uncover risk across systems, applications, and cloud environments.

View Services

Incident Response

When something goes wrong, clarity matters.We help you contain threats, coordinate response, and restore operations quickly, so your business can keep moving.

Explore Incident Response

Security leadership that strengthens your team

You don’t need more noise. You need clarity, direction, and experienced guidance.

We work alongside your team to help you prioritize risk, make informed decisions, and build a security program that supports your business.

Cyber Advisory

Risk assessments and program design to help you understand exposure and prioritize meaningful improvements.

vCISO Services

Experienced security leadership to guide strategy, align stakeholders, and support executive decision-making.

Data Security

Practical approaches to protecting sensitive and regulated data across modern environments.

Compliance that actually strengthens your security

Meeting regulatory and insurance requirements shouldn’t slow your business down or create a false sense of security.
‍
SecurIT360 helps you translate complex frameworks into practical controls, clear governance, and real-world security improvements.

Explore Compliance Services
Built for real-world operations
Focused on insurability and risk reduction
More than documentation
Coverage across key frameworks

A coordinated approach to staying operational

Strong security isn’t built from isolated tools or one-time assessments. It comes from understanding risk, validating what works, and responding with clarity when it matters.

We bring these elements together into a continuous, coordinated approach.

Understand

Identify where your organization is exposed across systems, workflows, and real-world attack paths.

Validate

Test whether your defenses actually work, not just whether they’re in place.

Respond

Contain threats quickly and coordinate response efforts to minimize disruption.

Guide

Strengthen decision-making, align stakeholders, and improve your security program over time.

Built for organizations that don’t have Fortune-500 security teams

Large vendors deliver complex platforms that require massive internal resources. Smaller providers deliver isolated services without strategic guidance.

We operate between those extremes.

SecurIT360 combines enterprise-level expertise with a hands-on, advisory-led approach, so your team gets the clarity, direction, and support needed to stay secure and operational.

Why organizations choose SecurIT360

Security isn’t just about tools or assessments. It’s about having the right expertise, the right approach, and a partner who understands how your business actually operates.

Practitioners, not just platforms

Our team brings real-world experience across offensive security, detection, and response, not just tool management.

You’re working with people who understand how attacks actually happen and how to stop them.

Security that fits your environment

We don’t force your organization into a predefined model.

Your security program is designed around your systems, workflows, and operational priorities.

A partner your team can rely on

We work alongside your internal team, not above it.

That means clear communication, practical guidance, and support when it matters most.

Focused on keeping you operational

Everything we do, from testing to response, is designed to reduce disruption and help your business keep moving.

Trusted by organizations where security can’t slow operations down

We uncovered risks we wouldn't have seen otherwise, got clear and actionable recommendations, and came away with a stronger and real sense of confidence in what we're doingwell.

Melissa, Information Security & Risk Manager
Midsize Law Firm

SecurIT360 made a very tedious and time-consuming process methodical and easy to navigate. Their team was organized, knowledgeable, and delivered a clear report leadership could actually use.

Lynn, Data Security Officer
Large Healthcare Network

The security assessments give us the backup we need to make effective change in our organization.... Plain and simple: They do what they say they are going to do when they say they are going to do it. Highly recommended.

Patrick, IT Security Manager
National Construction Firm

When organizations typically bring us in

Talk to an Expert

A recent incident raised questions about what’s working

Internal teams are stretched and need experienced guidance

Compliance expectations are increasing

Insurance requirements are getting harder to meet

Growth has outpaced internal capabilities

Insights from the field

Cybersecurity isn’t theoretical. It’s shaped by what actually happens in real environments.
‍
We share practical insights drawn from penetration testing, incident response, and day-to-day security operations—so you can make better decisions with real context.
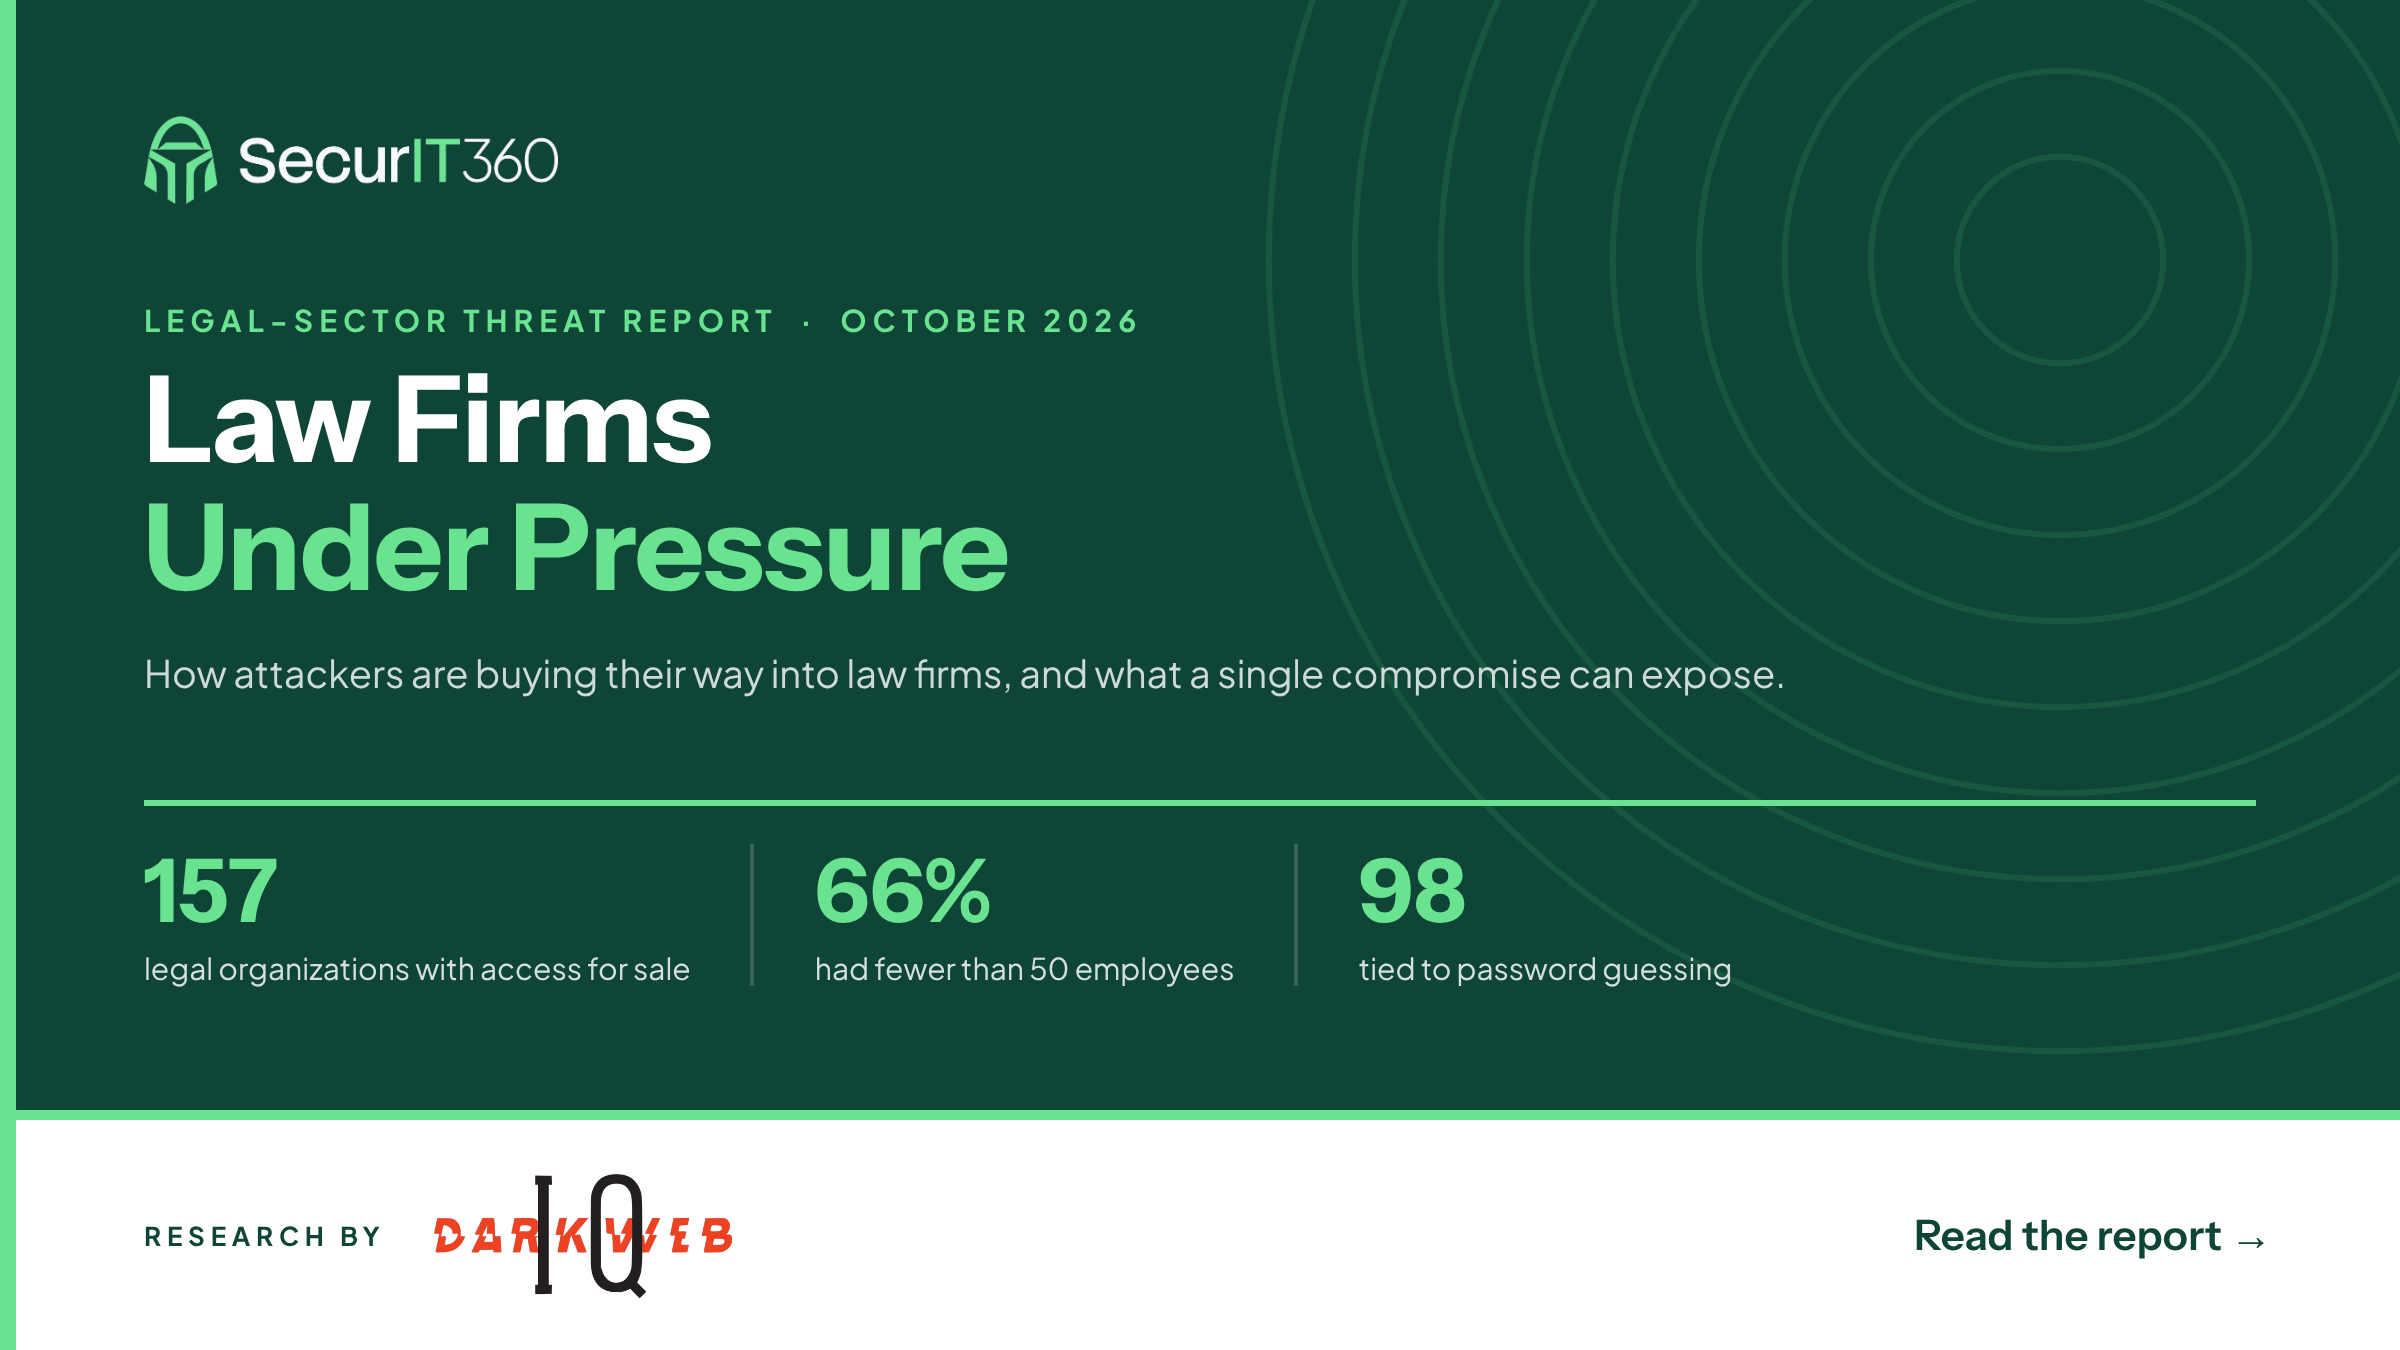
Law Firms Under Pressure: Legal-Sector Threat Report

Darkweb IQ research on 157 legal-sector organizations whose network access was offered for sale, and what a single compromise can expose.

Download

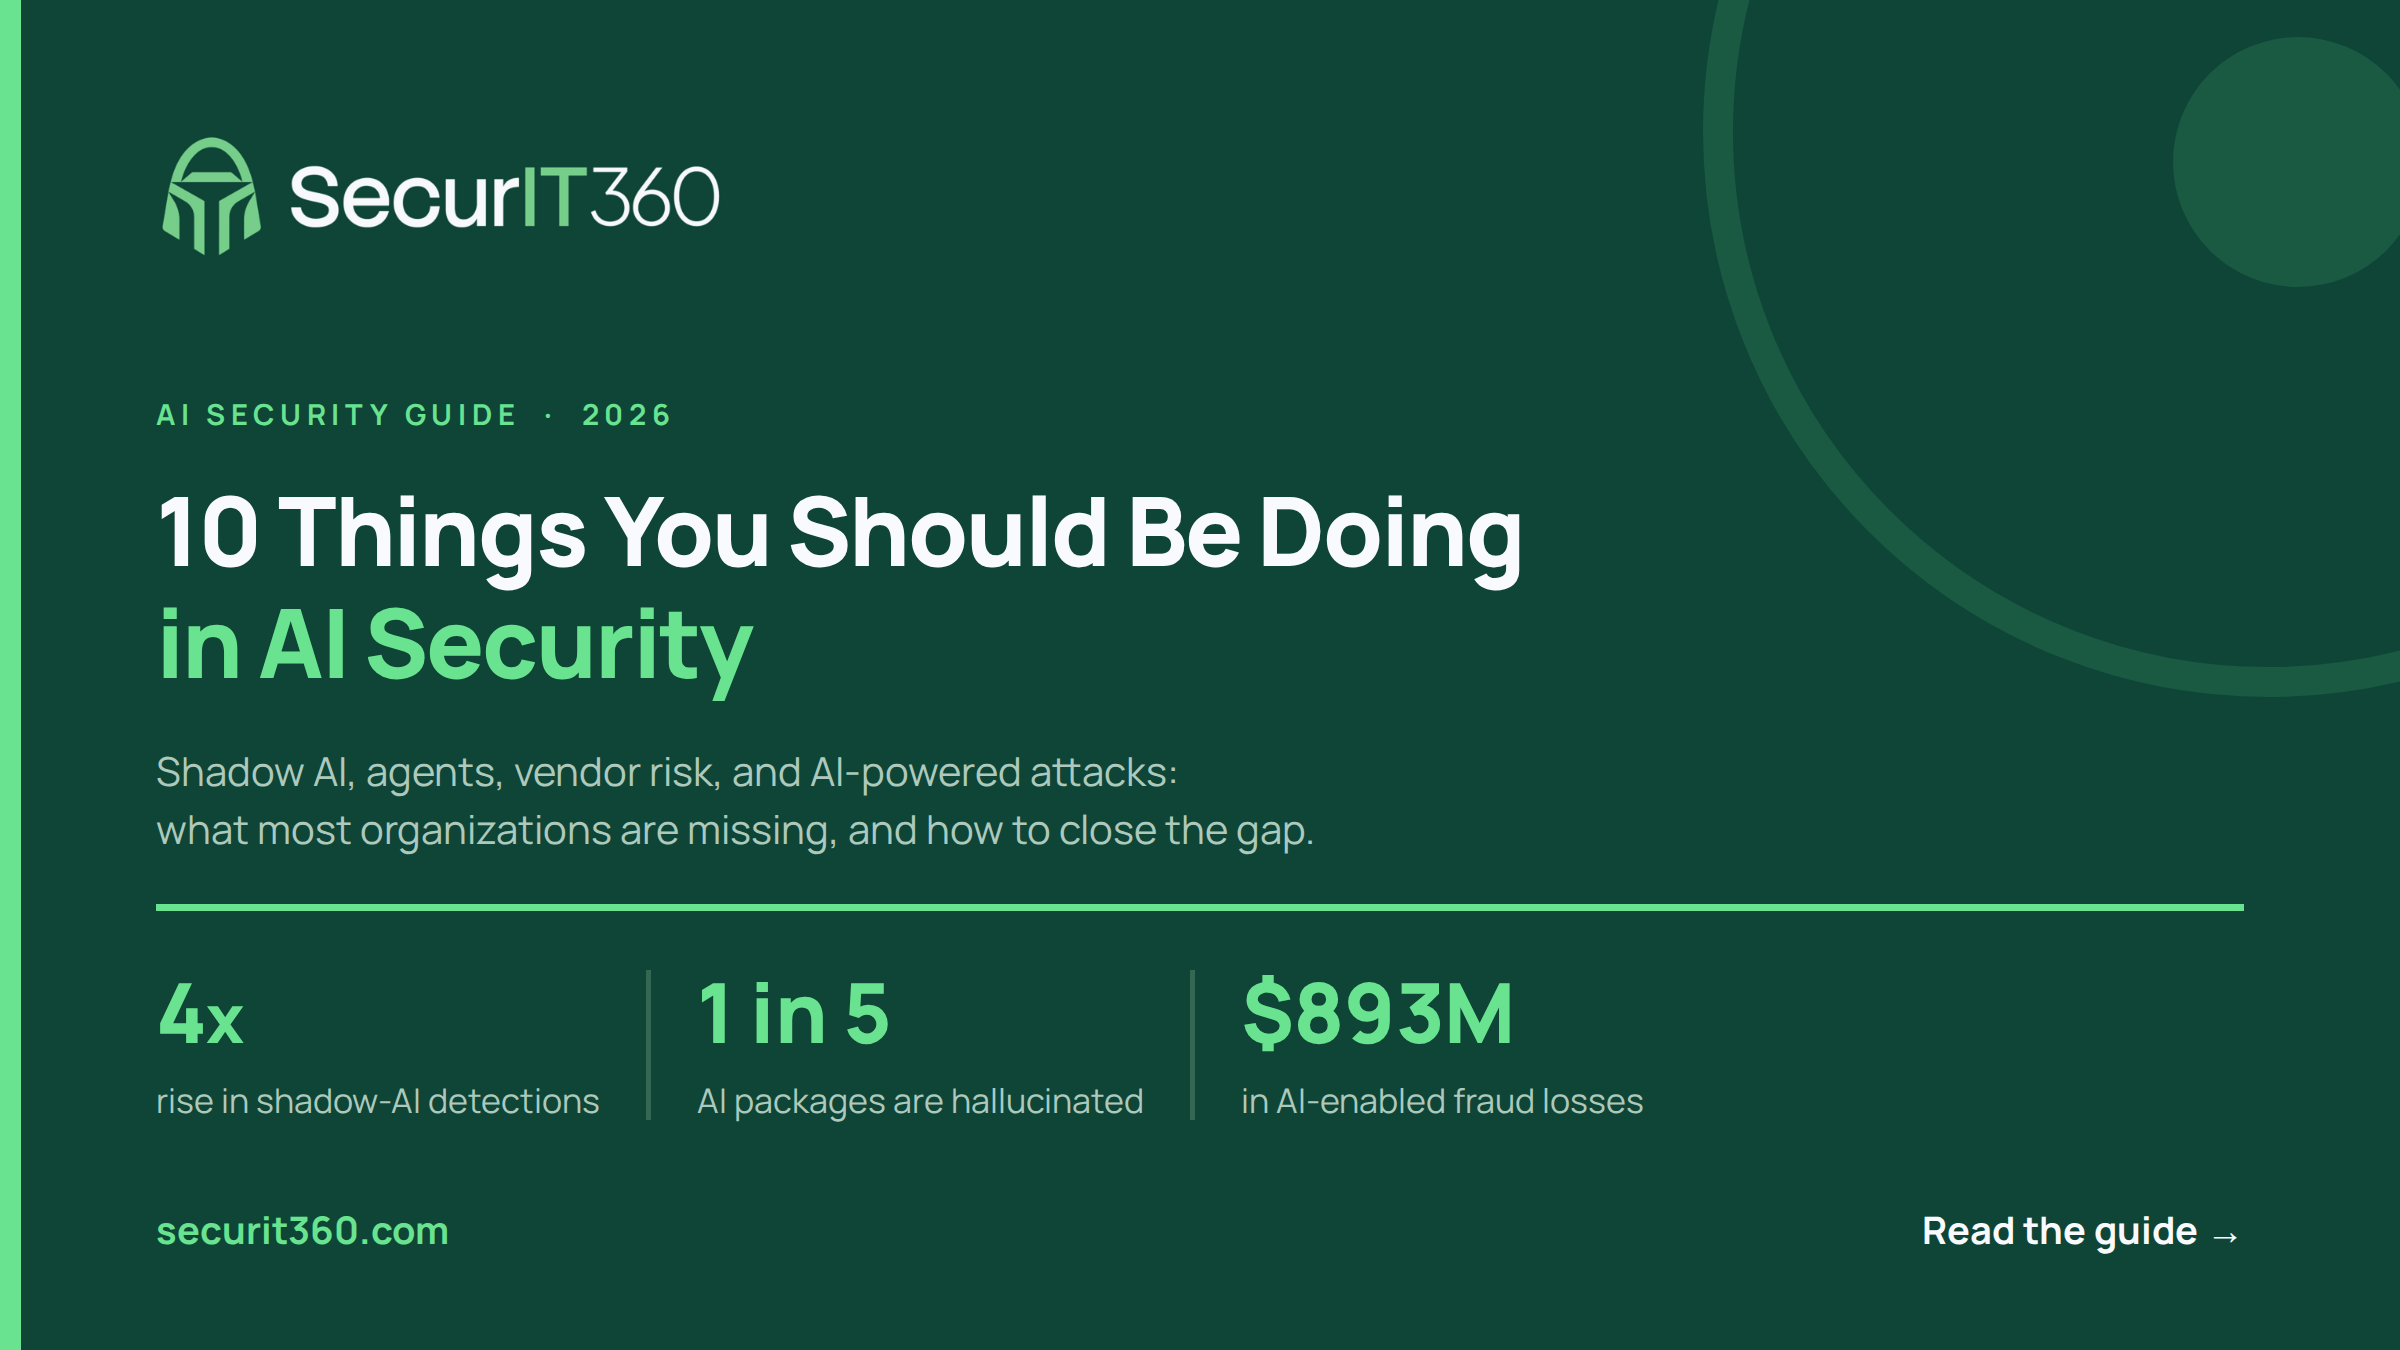
10 Things You Should Be Doing in AI Security

A practical checklist of ten steps law firms should take to secure AI use, from governance and tool inventory to access controls, testing, and monitoring.

Download

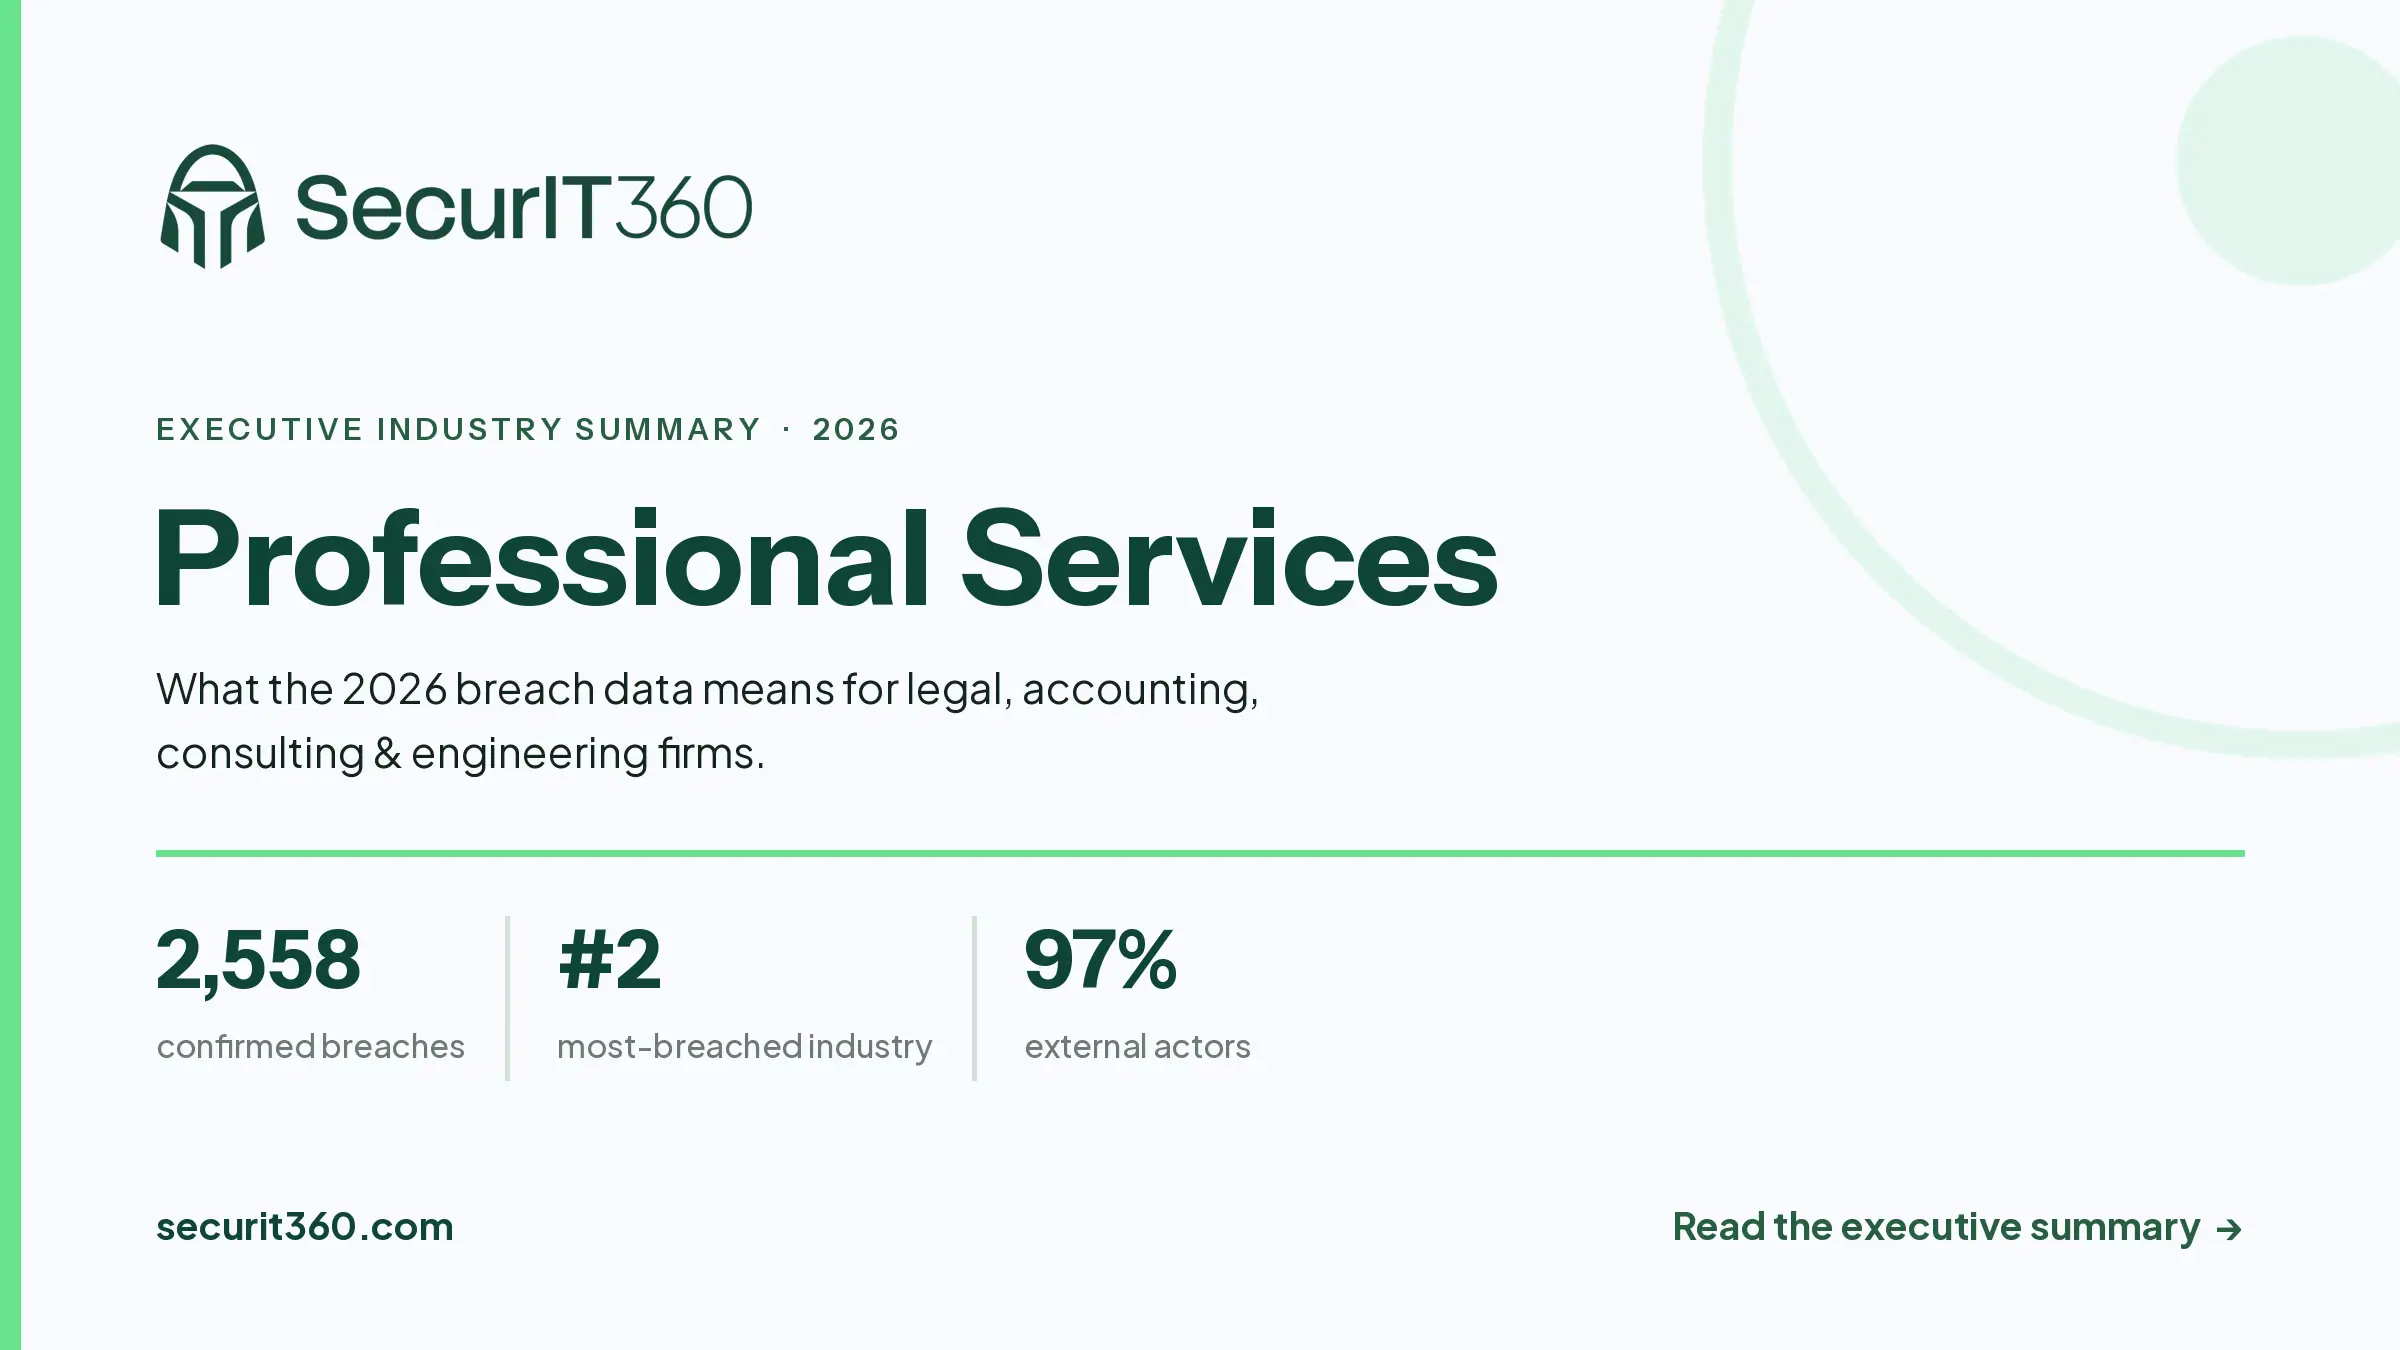
Professional Services: 2026 Cyber-Threat Landscape

Professional services was the second-most-breached industry in 2026, and the only major target left unprofiled in the year's most-cited breach research. Our executive summary fills that gap, translating the data into what it means for legal, accounting, consulting, and engineering firms.

Download

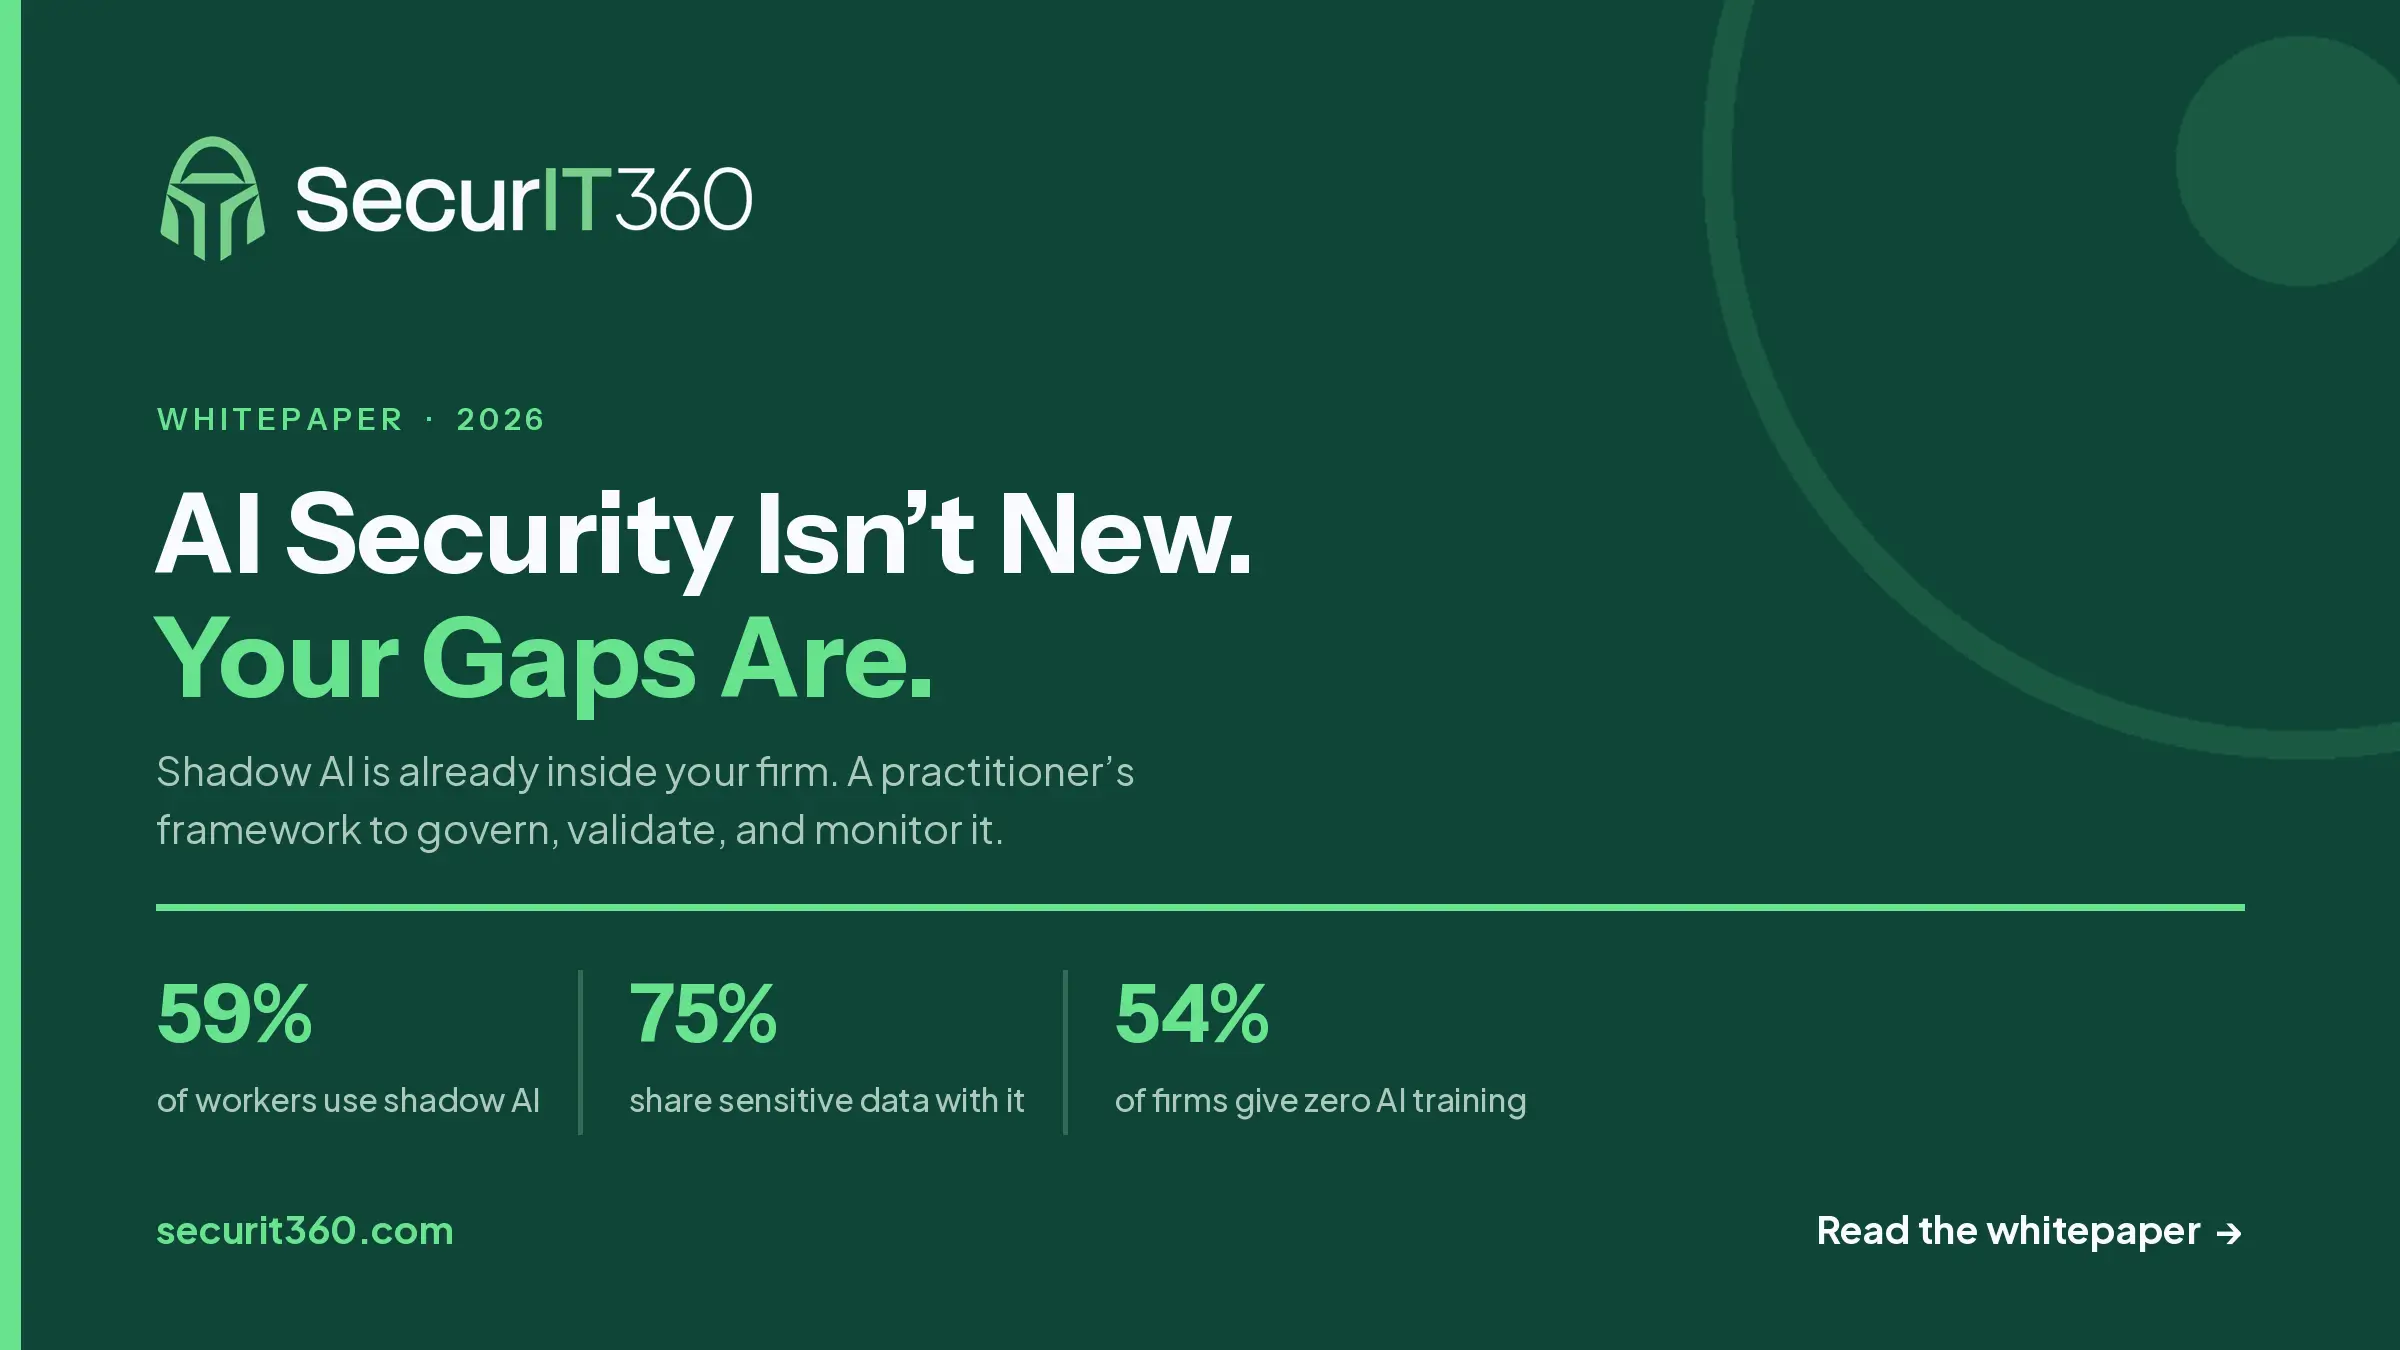
AI Security Isn't New. Your Gaps Are.

Most law firms don't have an AI security program. They have an AI security document. Learn why governance, testing, and monitoring must work together to protect privileged data and reduce AI risk.

Download
One Permission Away from Domain Takeover | Ep 201

One Permission Away from Domain Takeover | Ep 201

Discover how a single overlooked permission in Active Directory can put your entire domain at risk. This episode breaks down why dangerous permissions accumulate, what to look out for, and the real-world impact of these vulnerabilities.

Listen Now
OWASP Top 10 Part 6: Insecure Design and Business Logic Flaws Explained | Ep 200

OWASP Top 10 Part 6: Insecure Design and Business Logic Flaws Explained | Ep 200

Dive into the critical topic of insecure design and business logic flaws in web applications as discussed in this episode of The Cyber Threat Perspective. Learn how these vulnerabilities arise, real-world examples, and ways to prevent costly mistakes in your app development.

Listen Now
OWASP Top 10 Part 5: Injection Attacks and Real Pen Test War Stories | Ep 199

OWASP Top 10 Part 5: Injection Attacks and Real Pen Test War Stories | Ep 199

This episode of The Cyber Threat Perspective dives into the details of injection attacks, featuring real-world pen test stories and practical prevention tips. Brad and Jordan break down the OWASP Top 10 No. 5 risk and explain why it’s still a major concern for organizations.

Listen Now
Your Employee Got Hacked. Now What? | Ep 198

Your Employee Got Hacked. Now What? | Ep 198

What do you do after an employee gets hacked? In this episode, we break down a practical, post-compromise risk framework every defender should understand.

Listen Now
The Basics Still Win: What GreyNoise’s PaperCut Report Shows | Ep 197

The Basics Still Win: What GreyNoise’s PaperCut Report Shows | Ep 197

In this episode, we break down the recent GreyNoise PaperCut report and highlight why foundational security measures matter more than ever. Find out how attackers exploited vulnerabilities at scale and what defenses make the real difference.

Listen Now
One Hacker, 42 Targets: Inside Anthropic’s AI Threat Report | Ep 196

One Hacker, 42 Targets: Inside Anthropic’s AI Threat Report | Ep 196

Dive into Anthropic’s September 2026 threat report and see how AI is reshaping the cyber threat landscape. We break down the real-world impact, trends, and tactics behind AI-powered cyberattacks featured in the latest findings.

Listen Now
Every IT Team Has a Joe | Ep 195

Every IT Team Has a Joe | Ep 195

Every IT team has a “Joe,” the go-to admin who knows everything but creates big risks when too much knowledge is locked in one head. In this episode, we dig into the challenges of key man risk and offer actionable strategies to foster teamwork and resilience.

Listen Now
We Cracked Your 20-Character Service Account Password | Ep 194

We Cracked Your 20-Character Service Account Password | Ep 194

Service accounts are one of the most overlooked security gaps in Active Directory, and they’re a common path to domain admin for attackers. In this episode, we break down how these accounts are abused, why they’re risky, and what steps you can take to secure them.

Listen Now
Your IT Job Doubled. Nobody Told Your Boss. | Ep 193

Your IT Job Doubled. Nobody Told Your Boss. | Ep 193

Burnout in IT and cybersecurity is skyrocketing as workloads double and expectations keep rising. In this episode, we break down why this is happening and exactly how IT pros can advocate for themselves and stay effective.

Listen Now
Subtractive Security: Stop Adding Tools and Start Deleting Attack Paths | Ep 192

Subtractive Security: Stop Adding Tools and Start Deleting Attack Paths | Ep 192

Subtractive Security challenges the traditional approach of piling on security tools by focusing on removing unnecessary attack paths. In this episode, we break down the OWASP framework and explain how taking away can make you more secure than constantly adding.

Listen Now
Tuning CrowdStrike: The Settings Most Companies Never Turn On | Ep 191

Tuning CrowdStrike: The Settings Most Companies Never Turn On | Ep 191

In this episode, Spencer and Tyler break down the CrowdStrike configuration settings that make a real difference in detecting and blocking attacks. Skip the sales talk. Here’s what actually works based on thousands of hours of real-world testing.

Listen Now
OWASP Top 10 Part 4: Cryptographic Failures | Ep 190

OWASP Top 10 Part 4: Cryptographic Failures | Ep 190

This episode of The Cyber Threat Perspective breaks down “A04: Cryptographic Failures” from the OWASP Top 10 for web applications. Learn why many cryptographic issues are more about hygiene and reputation than real-world exploitation.

Listen Now
OWASP Top 10 Part 3: Software Supply Chain Failures — From SolarWinds to Vibe Coding | Episode 189

OWASP Top 10 Part 3: Software Supply Chain Failures — From SolarWinds to Vibe Coding | Episode 189

In this episode, the conversation focuses on software supply chain failures, now a top concern in the OWASP Top 10. Real-world examples and practical strategies are discussed to help organizations manage the risks of using third-party components and vendors.

Listen Now
Episode 188: Guaranteed Way to Catch Threat Actors

Episode 188: Guaranteed Way to Catch Threat Actors

In this episode, we break down how deploying cyber deception and honeypots can give defenders the upper hand against threat actors. Learn actionable strategies from active internal pen testers on guaranteeing early detection and improving your blue team’s effectiveness.

Listen Now
Episode 187: Avoid This Cyber Leadership Trap

Episode 187: Avoid This Cyber Leadership Trap

Avoid one of the biggest mistakes in cybersecurity leadership: buying tools before having a strategy. This episode breaks down a smarter approach that ensures security investments actually solve the right problems.

Listen Now
Episode 186: Real-Life Active Directory Attack Paths

Episode 186: Real-Life Active Directory Attack Paths

Join us as we break down real-life Active Directory attack paths uncovered during internal penetration tests. Learn how attackers exploit common misconfigurations and what you can do to defend your environment.

Listen Now
Episode 185 | A Toddler with a Bazooka: The Real Risk of AI Agents

Episode 185 | A Toddler with a Bazooka: The Real Risk of AI Agents

AI agents have moved far beyond chatbots and are now deeply woven into business operations, bringing new levels of risk and complexity. In this episode, we cut through the hype and break down what IT and security teams actually need to worry about.

Listen Now
Episode 184: Active Directory Isn’t Dead. It’s Just Undefended

Episode 184: Active Directory Isn’t Dead. It’s Just Undefended

Active Directory isn’t dead—it’s still powering the majority of organizations, and security risks are as critical as ever. In this episode, we dig into the real facts, common attack paths, and actionable defense strategies.

Listen Now
Episode 183: OWASP Top 10 Part 2 – Security Misconfigurations That Get You Hacked

Episode 183: OWASP Top 10 Part 2 – Security Misconfigurations That Get You Hacked

In this episode of The Cyber Threat Perspective, we continue our breakdown of the OWASP Top 10 by focusing on security misconfigurations. Learn why these vulnerabilities are common, how they happen, and what you can do to avoid them in your own web applications.

Listen Now
Episode 182: Patching Crisis — Vulns Now #1 Attack Vector (2026 Verizon DBIR)

Episode 182: Patching Crisis — Vulns Now #1 Attack Vector (2026 Verizon DBIR)

The 2026 Verizon Data Breach Investigations Report is out, and it’s time to break down what really matters for IT security teams. In this episode, we cut through the noise to highlight the new trends, major shifts, and actionable insights you need to know right now.

Listen Now
Episode 181: AI Zero-Days (Google Threat Intelligence Report)

Episode 181: AI Zero-Days (Google Threat Intelligence Report)

Google’s Threat Intelligence Group just dropped a game-changing report on the role of AI in modern cyber attacks. In this episode, we break down what’s new and what it means for defenders and organizations.

Listen Now
Episode 180: Cybersecurity Echo Chambers — How to Think Critically in a Hype-Driven Industry

Episode 180: Cybersecurity Echo Chambers — How to Think Critically in a Hype-Driven Industry

In this episode, we break down the dangers of echo chambers in cybersecurity and the importance of critical thinking in a hype-driven industry. Learn practical strategies to avoid falling into groupthink and make smarter decisions for your organization.

Listen Now

Let's Chat

Contact us now and we will get back to you same day.

If urgent, please provide your phone number.
‍
SecurIT360 helps you stay secure, operational, and prepared without adding unnecessary complexity.

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.